

|
|
|
If your organization’s security policies permit it, the device can be configured to work with measurement traffic outside the firewall and the management port inside (engine port can be either). See Figure 4.
Figure 4: CNA system spans the firewall
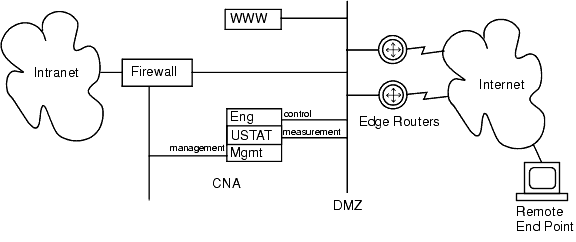
The management interface can be protected with access lists implemented on both your firewall and on the CNA system to define the type of access you want to allow through the management ethernet interface.
You can implement access lists on measurement interfaces to deny any traffic other than HTTP.
And, you can implement an access list on the engine ethernet interface to allow the edge routers to send packets during BGP sessions.
Figure 5: CNA system partially inside the firewall
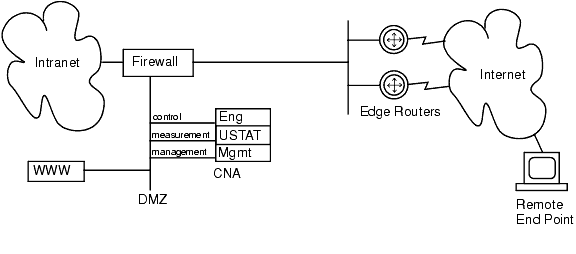
If you have given your web servers some firewall protection, you can place the CNA device on the same network and still be outside of your internal network.
|
|
|