

|
|
|
By adding multiple ISPs or tunnels at both ends of your private network, you can achieve the greatest measure of cost optimization and service reliability.
See Figure 5.
Figure 5: Optimized Multi-homed Hybrid Internet VPN / Private WAN
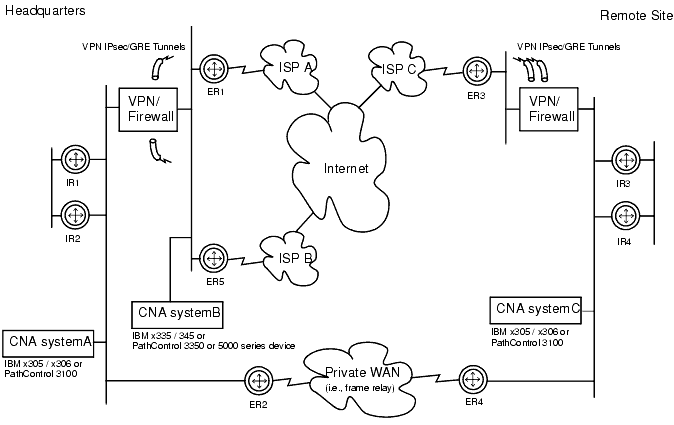
One CNA system sitting “inside,” behind your headquarters site VPN/Firewall device, decides whether your network traffic should go to the remote site through the VPN IPsec tunnel or through your private WAN circuit.
This device and the routers IR1, IR2, and ER2 are configured exactly the same as the headquarters equipment in the section Internet VPN and Private WAN Links.
A second CNA system (B in the diagram) sitting “outside” of your headquarters VPN/Firewall device is configured to optimize your IPsec tunnel and GRE tunnel endpoints. This CNA configuration is described above in the section VPN Tunnel Egress Optimization.
Traffic going through the VPN IPsec tunnel will then be routed through the best-performing ISP.
At your remote sites, an CNA system sits inside the VPN/Firewall and is configured as described in the section Internet VPN and Private WAN Links.
|
|
|